Skip to content
CardinalOps
  • Platform

    Platform

    • Threat Coverage Platform
    • Agentic Fleet
  • Use Cases

    Use Cases

    • Map all your detections to MITRE ATT&CK
    • Gain new detections to address critical gaps
    • Identify and fix broken detection rules
    • Pinpoint root causes of noisy rules
    • Continuous Threat Exposure Management (CTEM)
    • Operationalize threat intelligence
    • Measure the depth of ATT&CK coverage
    • Assess and improve your detection posture
    • Embed Detection Engineering into AI SOC
    • Manage detection posture across multiple SIEMs
  • Integrations
  • ROI & Pricing
  • Company

    Company

    • Who we are

      Meet the leadership team, advisors, investors, and mission that drive us forward.

    • Why work here

      Big challenges need big thinkers. Are you up to it?

    • Careers

      Your opportunity to make a difference … for our customers, the world, and yourself.

    • Security & Compliance

      We value the privacy and security of your data.

  • Resources

    Resources

    • Blog
    • Newsroom
    • Webinars & Events
    • White Papers
    • Videos
  • Contact Us
  • Book a Demo
HOME Resources
  • Blog
  • Newsroom
  • Webinars & Events
  • White Papers
  • Videos
  • What CISOs Don’t Know About Their SOCs

    What CISOs Don’t Know About Their SOCs

    In a recent SC Media column, Michael Mumcuoglu – CEO of CardinalOps, wrote how continuous improvement techniques can help CISOs more effectively manage the growing threat landscape and improve the visibility and effectiveness of their
  • Why MITRE ATT&CK Has Taken Over the SOC World

    Why MITRE ATT&CK Has Taken Over the SOC World

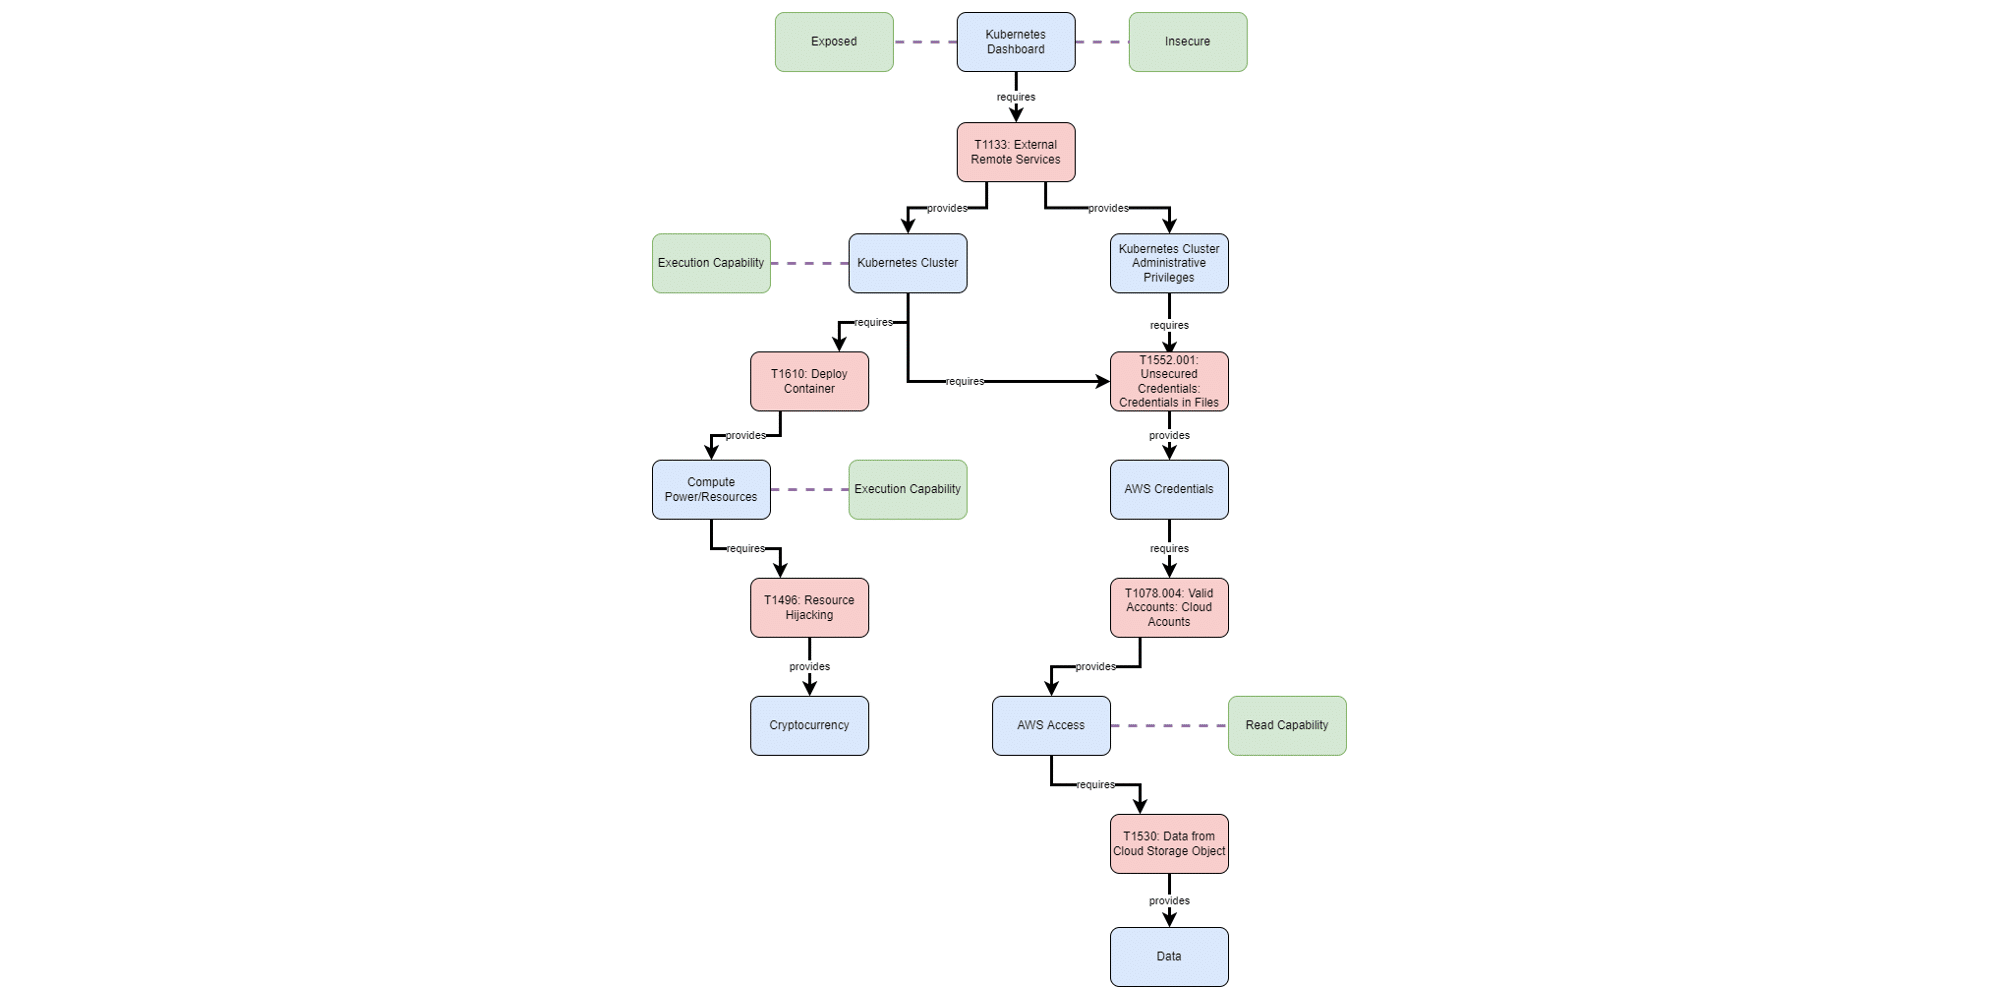
    I recently listened to an excellent summary about why MITRE ATT&CK has taken over the SOC world (sorry, it’s behind a paywall called “CSO Perspectives,” but this blog post is intended to summarize the key

  • Leveraging AI and Automation with MITRE ATT&CK to Eliminate Detection Coverage Gaps in Your SOC

    Leveraging AI and Automation with MITRE ATT&CK to Eliminate Detection Coverage Gaps in Your SOC

    At Black Hat 2022, our VP of Cyber Defense Strategy was interviewed on Security Guy TV to discuss why MITRE ATT&CK has become a standard way of describing your defensive posture to management as well

  • Enterprise SIEMs Detect Fewer Than 5 of Top 14 MITRE ATT&CK Adversary Techniques Used in the Wild

    Enterprise SIEMs Detect Fewer Than 5 of Top 14 MITRE ATT&CK Adversary Techniques Used in the Wild

    “Organizations need to become more intentional about detection in their SOCs. What should we detect? Do we have use cases for those scenarios? Do they actually work? Do they help my SOC analysts effectively triage

  • Dr. Anton Chuvakin answers questions about SIEM, EDR, and XDR — from our recent SANS webinar on the future of SIEM

    Dr. Anton Chuvakin answers questions about SIEM, EDR, and XDR — from our recent SANS webinar on the future of SIEM

    Dr. Anton Chuvakin Discusses “20 Years of SIEM – What’s Next?” Learn what Dr. Anton Chuvakin, Head of Security Solution Strategy at Google Cloud and former Gartner Research VP, has to say about questions like:

  • The Problem You Didn’t Know You Had – The Threat Coverage Gap

    The Problem You Didn’t Know You Had – The Threat Coverage Gap

    At CardinalOps, we talk to many, many security professionals about their security engineering practices, and their Security Information and Event Management (SIEM) solutions. The typical challenges we hear are:

  • Cloud Security Engineering – Automation to the Rescue!

    Cloud Security Engineering – Automation to the Rescue!

    Enterprises of all types and sizes are shifting to the cloud. Cloud related services, IaaS, PaaS, and SaaS are presenting new digital IT business opportunities with both short term and long term benefits. In fact,

  • The Comforting (or Discomforting?) Feeling of Objective Data Validation

    The Comforting (or Discomforting?) Feeling of Objective Data Validation

    It’s always nice to have conviction in your assumptions and hypotheses, but in the world we currently occupy there is a huge premium on truth, data and facts. I am, therefore, happy to announce the

  • “Hello World!” – the CardinalOps Coming Out Party!

    “Hello World!” – the CardinalOps Coming Out Party!

    We are thrilled to finally be able to share the story of what we’ve been working on for nearly a year. The story of how CardinalOps was founded.

  • CardinalOps Introduces Industry’s First Threat Coverage Optimization Platform

    CardinalOps Introduces Industry’s First Threat Coverage Optimization Platform

    [January 20, 2020, 8:00am Pacific Standard Time, USA]

  • Applying AI and Automation to a Surprisingly Unaddressed Security Function

    Applying AI and Automation to a Surprisingly Unaddressed Security Function

    In the cybersecurity market, we’ve seen fairly dramatic innovation over the past decade related to AI-based technologies–with much of that technology applied towards threat-detection techniques. Literally hundreds of startups have been funded in areas including

  • Security Products: Missing the ‘Out of Box’ Experience

    Security Products: Missing the ‘Out of Box’ Experience

    What do firewalls, SIEM, SOAR, and many other cyber security products all have in common? Apart from the obvious answer, that they all protect enterprises against threats one way or the other, I see one

Previous Page
1 2 3 4
Next Page

Never Miss Another Threat

CardinalOps’ Agentic Detection Engineering represents a fundamental shift in how detection engineering operates. Instead of relying solely on manual effort, it introduces a coordinated system of specialized AI agents that optimize the entire detection lifecycle and fly alongside human detection engineers.

Detection teams can scale without adding headcount. Alert fatigue gives way to signal clarity. Detection lifecycle management becomes streamlined instead of sprawling. Feedback from the SOC finally closes the loop to create better detections over time. 

See it for yourself.

Book a Demo
CardinalOps

Optimize your cyber defense with AI-powered detection engineering.

  • Use Cases
  • Integrations
  • Company
  • Resources

© 2026 CardinalOps

Privacy Policy | Terms & Conditions | Security & Compliance